Command overview
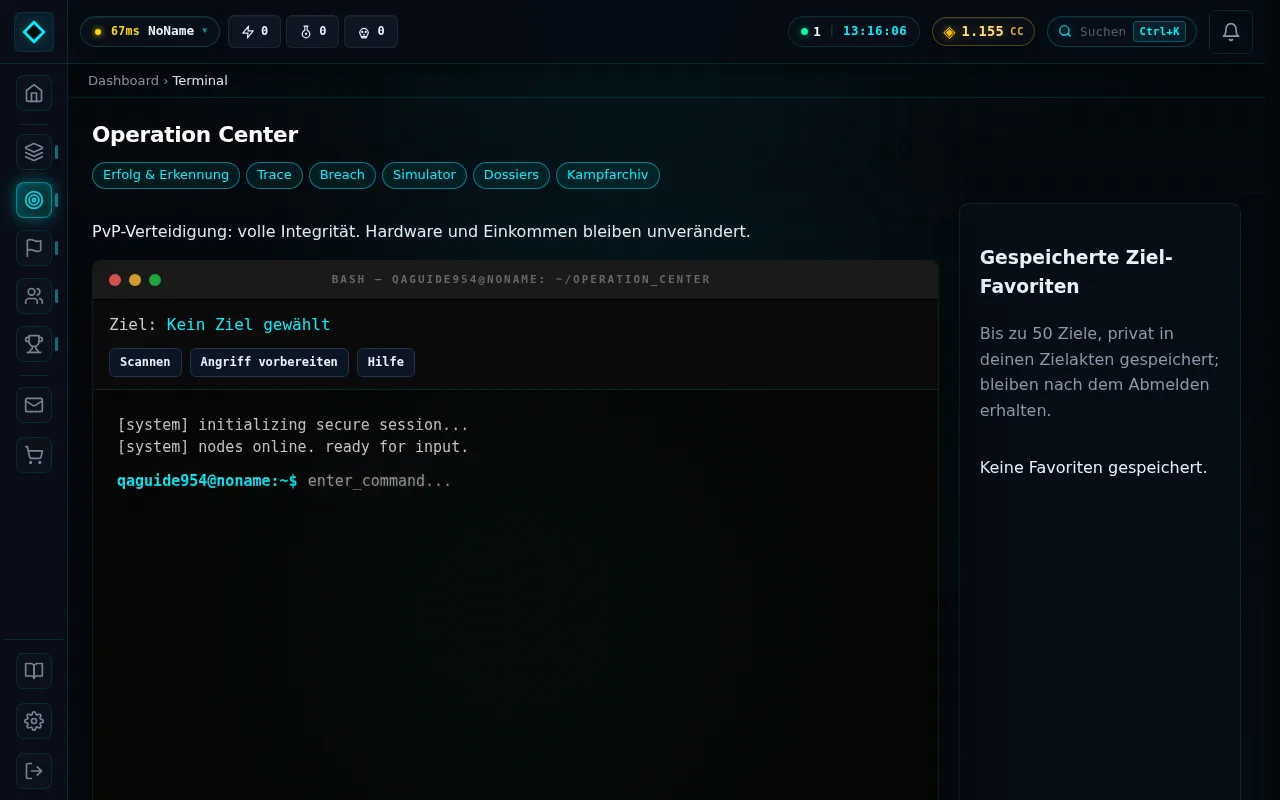
The terminal in the operation center accepts commands for recon, attack, forensics and system info. Probing a target or opening this help does not start an attack; only a confirmed action counts. The table lists all available commands with their syntax.
| Command | Description |
|---|---|
| attack <target> [opt] | Manual attack with module specification |
| clear | Clear terminal output |
| help | Show command overview |
| hping3 <target> | Packet flood to paralyze a server (ddos) |
| implant <target> | Rootkit installation for surveillance |
| metasploit <target> | System exploit for hardware sabotage (breach) |
| nmap <target> | Public /24 node list, not a port scan. Host IP, short IP, subnet number, network prefix, .x, .* or /24; other masks and options are rejected. |
| probe <target> | Public /24 node list (nmap alias). A host IP selects its subnet; no ports or options. |
| sqlmap <target> | Automated exploit for siphoning CC (drain) |
| takeover <target> | Take over a server permanently (also: attack <target> takeover). Core framework 3, zero-day exploit 1, fee also on failure, confirm with confirm. |
| bounty | Show darknet bounties & syndicate contracts |
| ifconfig | Show your own server's network configuration |
| uptime | Show session uptime since the last login, not historical account age. |
| whois [target] | Retrieve player information and rank |
| breach | Open the breach minigame as a practice puzzle (no target, no game effect). |
| netstat | Active network connections and attack logs |
| ps | Show running processes (upgrades, research) |
| scrub <log_id> | Erase your own digital attack traces on foreign systems |
| top | Top player ranking in real time |
| trace <log_id> | Forensic analysis and reconstruction of foreign attacker IPs |
| upgrade [hardware] | Start a hardware upgrade or show the overview |